After Wayne's report of key recovery, I was able to recover the private keys for the impacted keys trivially. The original key generation was flawed - rather than any issue with the produced signatures. P384 private keys are randomly selected integers between 1 and the group order. The 8 impacted keys all used integers less than 256. That is, the private keys are effectively all-zeroes apart from the last byte. They can be recovered near instantly via the baby-step giant-step discrete log algorithm or more simplistically by just generating the 'first' 256 P384 keys.
Single byte private keys live for 18 months, can be generated by anyone locally.
No sign of a fake web TLS cert being issued as per CT logs but I wonder how many fake Windows code signing, PDF signing etc. certs would have been issued and used actively.
Browsers(even non-updated ones) would mostly be safe as they already fetch revocation lists without any software updates but going forward any non-browser tools running on a non-updated client could easily be MITMed by anyone in network path.
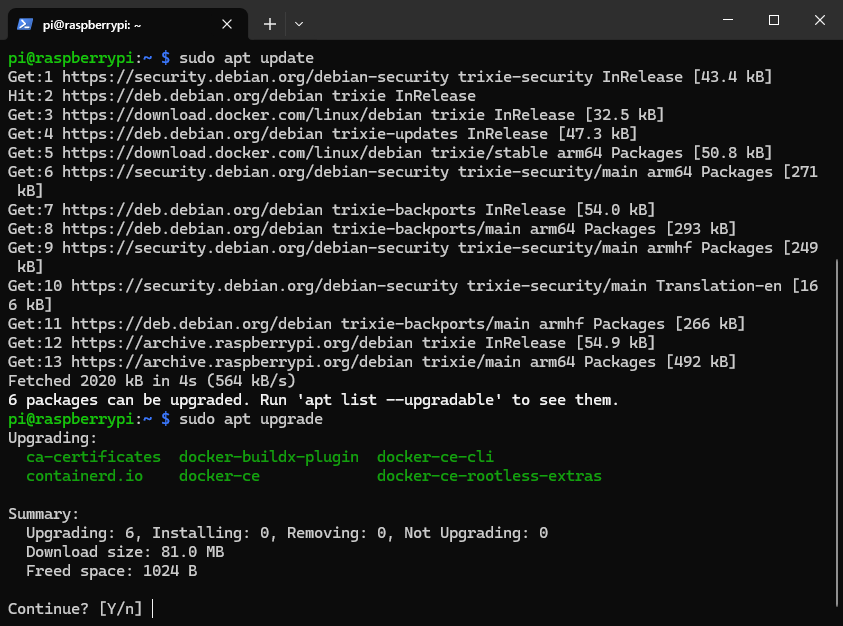
Lol my Debian mini PC auto upgraded itself this morning daily update check to replace the ca-crrtificates package, my rpi4 running ubuntu server might do the same hopefully today morning itself
Following the discovery that eight eMudhra intermediate certificates use weak keys, Cloudflare is deploying mitigations and releasing client updates. We explain the impact, our response, and what customers and developers should do next.
This website uses affiliate links. This means that if you click on a link and make a purchase, we may receive a commission. This does not affect the price you pay for the product.
This site uses cookies to help personalise content, tailor your experience and to keep you logged in if you register.
By continuing to use this site, you are consenting to our use of cookies.
 bugzilla.mozilla.org